Security Architecture
Enterprise-grade security built from the ground up. VaultKey is designed, built, and operated with security as the primary consideration.
Security Foundations
Encryption Standards
All data is encrypted using military-grade cryptographic algorithms meeting NIST standards.
- • At Rest: AES-256-GCM encryption for all stored secrets
- • In Transit: TLS 1.3 for all network communication
- • Key Management: PKIX-compliant key infrastructure
- • Envelope Encryption: Secrets encrypted with unique keys
Access Control
Fine-grained access control prevents unauthorized access at every level.
- • Role-Based Access Control (RBAC) with custom roles
- • Attribute-Based Access Control (ABAC) for advanced policies
- • Identity verification using mTLS and JWT
- • Service-to-service authentication with API keys
Infrastructure Security
VaultKey is deployed in isolated, hardened environments with strict network controls.
- • Dedicated AWS VPCs with no internet exposure
- • Hardware security module (HSM) backed key storage
- • DDoS protection and rate limiting
- • Regular penetration testing by certified firms
Compliance & Certifications
VaultKey meets the strictest regulatory and compliance requirements.
- • SOC 2 Type II certified
- • ISO 27001 certified
- • HIPAA compliant deployments available
- • PCI-DSS certified for payment processing
Incident Response
24/7 monitoring and rapid response to any security incidents.
- • Continuous security monitoring and alerting
- • 24/7 Security Operations Center (SOC)
- • Formal incident response procedures
- • Breach notification within 24 hours
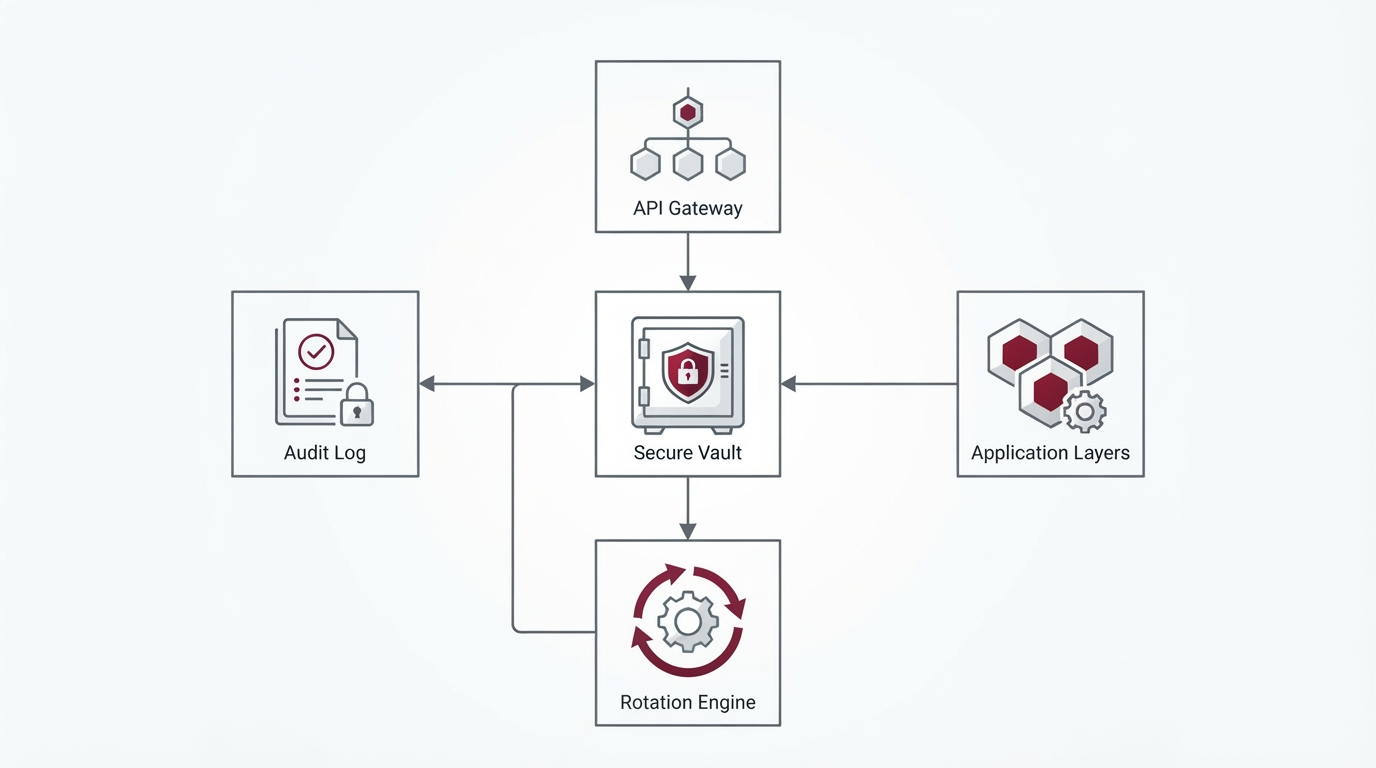
System Architecture Diagram
Threat Model & Mitigation
Threat: Unauthorized Access
Mitigation: Multi-layered access control with RBAC, ABAC, MFA, IP restrictions, and time-based access limits. Every access attempt is logged and audited.
Threat: Data Breach
Mitigation: Military-grade AES-256 encryption, envelope encryption with separate key storage, HSM integration, and encrypted backups. Data is always protected even if storage is compromised.
Threat: Man-in-the-Middle Attack
Mitigation: TLS 1.3 for all traffic, certificate pinning, mTLS authentication, and cryptographic verification of all communications. Zero tolerance for unencrypted data transmission.
Threat: Insider Threat
Mitigation: Immutable audit trails, principle of least privilege, separation of duties, background checks, and continuous monitoring of privileged operations.
Security Documentation
Download our comprehensive security white paper and compliance documentation.